UAE Cyber Security Council Intercepts 300,000 Attacks During UN Crime Congress with 90 Percent Driven by Artificial Intelligence
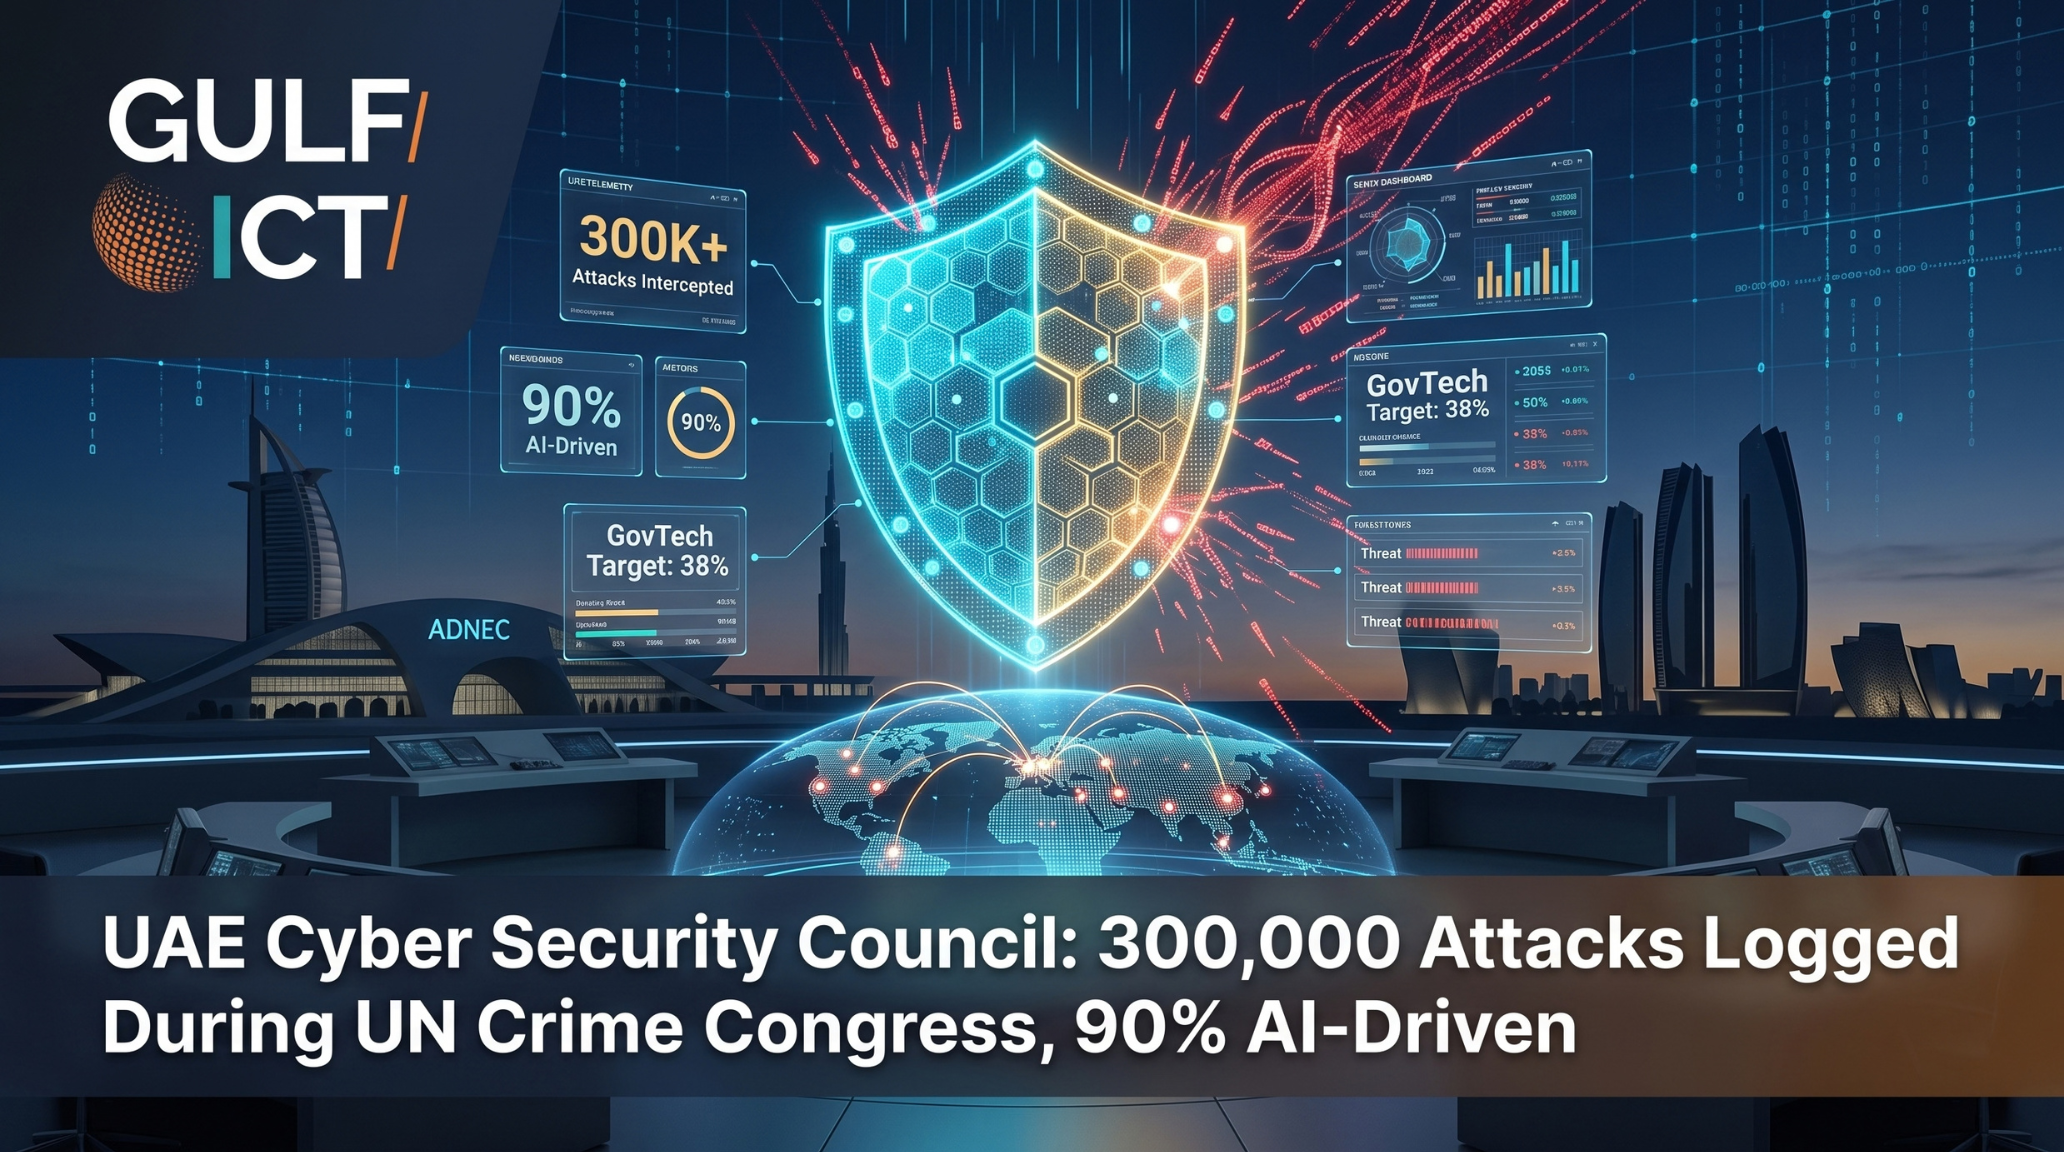
ABU DHABI — The UAE Cyber Security Council has disclosed that approximately 90 percent of tracked cyberattacks targeting the country are powered by artificial intelligence tools and automated agentic scripts, recording over 300,000 cyber attacks within forty eight hours of the opening of the 15th United Nations Congress on Crime Prevention and Criminal Justice in Abu Dhabi.
Presenting live threat telemetry from its operational exhibition pavilion at the ADNEC Centre, council officials revealed that nationwide attack volumes fluctuate continuously, scaling up to 600,000 cyber attacks per day during peak threat cycles. The council emphasized that persistent, real time behavioral surveillance has become the definitive line of defense as threat actors increasingly weaponize cognitive systems, generative reconnaissance, and automated vulnerability exploitation pipelines.
Institutional telemetry data shows public sector entities sustained the heaviest concentration of attacks, with government entities absorbing 38 percent of all recorded incidents. Educational institutions ranked second at 23 percent, followed by the financial sector at 16 percent, the energy sector at 14 percent, transport infrastructure at 5 percent, and healthcare networks at 4 percent.
Evaluating attack severity profiles, the council categorized 54 percent of tracked incidents as low risk, 29 percent as medium risk, 9 percent as high risk, and 8 percent within the critical severity tier. Parallel telemetry tracking software vulnerability disclosures revealed that 29 percent reflected high severity vectors, while 5 percent fell into the critical category.
Geographic origin mapping identified the United States, Brazil, the United Kingdom, Germany, and Argentina among the most prominent launch jurisdictions, with Brazil accounting for 9 percent, the United Kingdom 4 percent, and Germany and Argentina 3 percent each. Across active threat intelligence categories, the monitoring matrix logged 273 threat indicators, approximately 1,800 active campaigns, and 1,090 distinct threat signatures.
Addressing a concurrent session on disrupting transnational financial networks, Middle East and North Africa Financial Action Task Force (MENAFATF) President Hamid Saif Al Zaabi affirmed that strengthening cross border defense against illicit finance requires institutional coordination, converting supervisory assessments into operational results that systematically sever organized crime syndicates from digital liquidity.